

Items tagged with security
Remember over a year ago when we reported on the ClickFix malware that uses fake CAPTCHA mechanisms to dupe unwitting victims into pwning their own machines? Well, apparently not enough people shared that post, because the problem has...
Read more...
It appears a vulnerability exists within MacOS's WebGPU implementation that can crash a system with a few simple commands, Auberon López (aka @auberonedu on GitHub) revealed this week.
Auberon's day job is as an instructor at the Green...
Read more...

Microsoft broke its previous Patch Tuesday record with yet another record-setter this week. September's Patch Tuesday will contain 974 total fixes, with 113 of them rated "Critical" for high likelihood of exploitation. So far this year...
Read more...

The security research team at Zimperium’s zLabs has uncovered a new strain of malware targeting Android devices, which not only looks to pilfer a victim’s data but also inflict maximum psychological damage. It has been dubbed 'Mantax Otax'...
Read more...
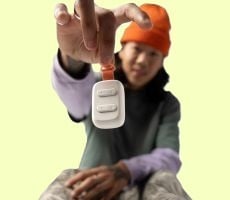
A security flaw in Skullcandy's Dime 3 wireless earphones allows nearby attackers to hijack Bluetooth connections, intercept audio playback, and access built-in microphones without any user interaction or physical confirmation.
To be...
Read more...
Google has begun pushing out Chrome 153 across Windows, macOS, Linux, Android, and iOS, arriving right on the heels of an emergency security patch. This release marks the start of its new two-week major milestone update schedule. First...
Read more...
Keyword smuggling, which is the practice of obfuscating spam keywords to bypass detection filters, has been common practice for quite some time. Microsoft is warning that this traditional tactic has been enhanced by a new-school method of...
Read more...
Google has issued an emergency security update for desktop Chrome users across Windows, Mac, and Linux to address a dozen high- and medium-severity vulnerabilities. One of them is a zero-day flaw that Google confirms is being actively...
Read more...
Microsoft Threat Intelligence has discovered a new variant of the ClickFix malware campaign we covered last year, and it's been dubbed "TerminalFix." The fundamental nature of the attack is similar in the sense that it also relies on false...
Read more...
Federal law enforcement has dismantled a major Chinese state-sponsored cyber-espionage apparatus that targeted critical infrastructure and key government agencies across the United States for nearly eight years. It also makes us wonder...
Read more...
Uh-oh, e-commerce giant AliExpress has been caught running hidden, silent audio processes inside visitors' browsers to generate unique device tracking profiles without user consent.
This naughty deed was uncovered after software...
Read more...
Cybersecurity researchers at Kaspersky have uncovered a malware downloader that targets Android-based automotive head units, marking the first documented case of malicious code explicitly engineered to compromise vehicle infotainment...
Read more...
Municipal public comment periods are usually home to standard local grievances, but a recent San Diego City Council meeting received an Imperial visit when Darth Vader stepped up to endorse Flock cameras and automated surveillance...
Read more...

Researchers from the University of Massachusetts Amherst have uncovered a critical security flaw in contactless payment processing that allows expired credit cards to be reanimated and used for fraudulent purchases.
Presented at the USENIX Security 2026 conference, the UMass researchers...
Read more...

Microsoft nemesis Nightmare-Eclipse is at it again, this time with a bypass exploit for his original RoguePlanet Windows Defender privilege escalation exploit. The new exploit, dubbed ShieldBreak, also allows for elevation of privilege...
Read more...

The National Cyber Security Centrum (NCSC) of the Netherlands says it has evidence that hackers are actively exploiting a vulnerability in one of macOS’ sharing features, which can provide attackers with complete access over a victim’s...
Read more...

Apple has issued high-confidence threat notifications to targeted users across 110 countries, warning that their devices may have been targeted by sophisticated mercenary spyware attacks.
The global alert is Cupertino's latest push to...
Read more...

ASUS has patched another serious security vulnerability in Armoury Crate and several other hardware-management utilities that could let an unprivileged application gain kernel-level access on Windows systems. The vulnerability, tracked as...
Read more...

If your phone has been spared an endless barrage of sketchy pop-ups, phishing scams, and fake security warnings lately, you have Google's multi-layered browser defenses to thank. In a recent security deep dive, Google claims that Chrome’s...
Read more...
Microsoft has discovered a Russian malware campaign called CaptiveCrunch, which is designed to compromise users of public Wi-Fi with falsified prompts at the captive sign-in screen. This includes phishing pages that steal logins or even falsified Windows or Android system update/download...
Read more...

Cybersecurity researchers at Palo Alto Networks' Unit 42 have uncovered three novel post-compromise attack vectors that allow local malware on Windows PCs to quietly hijack Google-synced passkeys, bypassing biometric checks and PIN...
Read more...

Generative AI has drastically lowered the bar for finding software vulnerabilities, but it has simultaneously unleashed a flood of machine-generated noise that is overloading security teams and breaking bug bounty programs.
According...
Read more...