

A new piece of Windows malware is making the rounds, but what else is new? You never want to fall victim to a malware campaign, but this one is particularly troublesome. EvilExtractor is billed as an "all-in-one" solution for your online...
Read more...
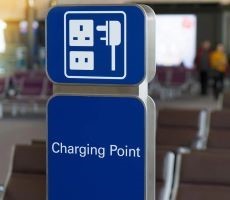
The FBI just issued a warning to the public against using free public USB charging ports, such as those found at airports or malls, because they've been found to be ports of entry for malware.
A recent tweet by the FBI Denver field...
Read more...
Time to tighten up your password complexity, dear readers. A deep learning password guessing tool called PassGAN has been found to take less than six minutes to crack your seven-character password, even ones with symbols.
Nefarious...
Read more...
Google wants its Play Store users to have more control over their app account data by allowing them to delete their account and/or data directly within the app or online. Chalk that up as a nice win for personal data privacy.
In an...
Read more...
Storage heavyweight Western Digitial announced over the weekend that it has suffered a "network security incident," which is a less alarming way to say its systems have been hacked by unknown threat actors. The company says it is currently...
Read more...
Google used to offer Nexus-branded Android phones, but now Nexus means mobile malware. Chatter about the Nexus banking botnet began appearing on hacking forums in January 2023, but security researchers from Cleafy now believe this Android...
Read more...
A highly malicious malware is infecting Intel- and M-powered Macs, stealing sensitive information such as user passwords, credit card info, and cookies.
Uptycs researchers recently uncovered a new malware that targets macOS desktop and...
Read more...
Security experts confirmed a major bug in a core Windows app last week, and Microsoft is already rolling out a fix. As we learned recently, the Windows 11 Snipping Tool was susceptible to the "Acropalypse" bug initially discovered in...
Read more...
When you delete something, you would naturally expect it to stay deleted. With the "acropalypse" bug, all bets are off. Security researchers discovered last week that Google's Pixel phones would retain data from cropped screenshots...
Read more...
Famed automaker Ferrari announced yesterday that the company suffered a data breach involving personal information of its clients, without any impact on its operations.
A hacker or hackers were recently able to gain access to the...
Read more...
Amazon-owned Ring is one of the largest providers of smart home cameras and security products, but any users who were trying to get by with the free service tier might be looking to jump ship soon. According to notices sent out by Ring...
Read more...
Mortal Kombat has a reputation for being brutal, but rather than exacting excessive violence on video game characters, unknown threat actors are brazenly brutalizing their victims’ finances in a Mortal Kombat-themed ransomware campaign...
Read more...
Scammers are real pieces of...work (substitute any word you like) as they rarely display any scruples—they prey on the elderly, think nothing of wiping out someone's hard-earned life savings, and are opportunistic predators. That latter...
Read more...
Pepsi Bottling Ventures (PBV) has suffered a major data breach, with hackers making off with a trove of sensitive information. The company has begun notifying affected individuals of this incident, but the details remain sparse. According...
Read more...
Last year saw a rise in threat actors abusing Microsoft Office macros to infect their victims’ systems with malware, prompting Microsoft to block macros embedded in documents downloaded from the internet. In response, threat actors have...
Read more...
We often report on phishing campaigns involving fraudulent customer support agents who trick victims into giving up sensitive information or installing malware on their systems. However, sometimes threat actors flip this script, instead...
Read more...
The password manager KeePass is currently the subject of a debate concerning whether or not a particular design decision should be considered a security vulnerability. At the center of this debate is KeePass’ support of triggers, one of...
Read more...
Earlier this month, a Swiss hacker who goes by the name maia arson crimew exfiltrated a copy the US government’s No Fly List from an insecure server. This list, which names individuals who are forbidden from flying anywhere within US...
Read more...
Last November, two weeks after the Biden administration held the second International Counter Ransomware Summit, the Federal Bureau of Investigation (FBI), the Cybersecurity and Infrastructure Security Agency (CISA), and the Department of...
Read more...
Yesterday, the Cybersecurity and Infrastructure Security Agency (CISA), the National Security Agency (NSA), and the Multi-State Information Sharing and Analysis Center (MS-ISAC) published a joint cybersecurity advisory warning network...
Read more...
TA444 is an advanced persistent threat (APT) group believed to be associated with the North Korean government. However, rather than receiving financial backing from its government, the group seems to bring in revenue for the government...
Read more...
Over the past week, Gmail users have been reporting abuse of the Google Ads platform. However, rather than conducting ad fraud or placing ads that distribute malware, the actors behind this recent activity are leveraging the Google Ads...
Read more...