

Items tagged with Malware

Just when you thought it was safe to tweet again, another Twitter worm has reared its ugly head. In case you were busy hunting for Easter eggs or biting the heads off chocolate bunnies this weekend, and didn't have a chance to tweet or read other folks' tweets on Twitter, the micro-blogging social-networking site was hit with no less than...
Read more...

Since the April 1st Conficker target date came and went, people have been waiting for the other shoe to drop. And on Wednesday night, Conficker downloaded the update that people were expecting, via the P2P functionality that's part of the malware.Dubbed Conficker.e, the new version appears to focus on that all-too-familiar item that malware...
Read more...
We had all been warned: April 1 was the day that the infamous DOWNAD/Conficker worm was supposed to activate and do its dastardly deeds, whatever they might be. The day came and went without a whimper of Conficker-initiated destruction, although that didn't stop countless media outlets from reporting on it (HotHardware included). Conficker...
Read more...

April 1st has come and gone, but researchers are convinced we haven't seen the last of the Conficker worm. While there are ways to determine if you are infected, the Conficker Working Group has posted a simple and visual aid to help as well. The Conficker Working Group is a group of organizations that have joined forces to fight the Conficker...
Read more...

60 Minutes is a great show, for the most part (and let's not forget it has Andy Rooney!), but a report Sunday night on the Conficker worm titled "The Internet is Infected" is probably the definition of hyperbole. The report, a full transcript of which is here, and a video below, was designed to alarm, and I'm sure it did. The title alone is...
Read more...
After a 10-month cyber espionage investigation, researchers have found 1,295 computers in 103 countries with software that is capable of stealing information from high-profile targets such as the Dalai Lama and government agencies around the world. In the report published today by Information...
Read more...

TinyURL is a popular URL shortening service which is frequently used to reduce the length of a URL to something more manageable. Security firm Trend Micro has warned that TinyURL phishing, first reported in February, is becoming more popular and spreading across different languages. An example of tinyURL use would be perhaps a Mapquest link...
Read more...
Internet security and infrastructure service provider, OpenDNS, and security software provider, Kaspersky Lab, have collaborated to help alert users that their systems are infected by one of the "most widely-spread" worms to come our way, the Conficker worm. The Conficker worm, which is also called Kido and Downadup, first popped up "in late...
Read more...
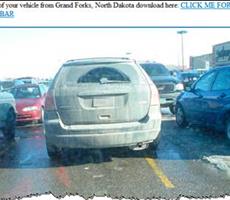
Using a combination of social engineering and malicious software, an innovative new way to get people to install malware on their computers has recently popped up, and it all starts with finding a flier on your car's windshield stating that your car is illegally parked. The fliers are fake...
Read more...

Security software company, AVG Technologies, reports that as many as 300,000 new, unique Websites launch every day, whose sole purpose is to infect visiting computers with malware. Not only has this number jumped up from as many as 200,000 only three months earlier, but many of these sites...
Read more...

Mac-based security software company, Intego, is warning that a Trojan horse targeting Macs is actively out in the wild and that at least 20,000 users have already downloaded (although not necessarily installed) infected software. The Trojan horse has the name OSX.Trojan.iServices.A and it is piggybacking on pirated copies of Apple's new iWork...
Read more...

Lavasoft, developer of the long-time entrant in the spyware detection arena, Ad-Aware, has released a stand-alone antivirus application. The new product, Lavasoft Anti-Virus Helix is based on technology from antivirus vendor Avira. It's interesting that Lavasoft would make this move shortly after Microsoft's announcement to drop OneCare and...
Read more...

It's long been asserted that Apple computers are invulnerable to viruses. This has not been because the OS is flawless, but rather because hackers focused on the more popular OS: Windows, as well as the fact that most hackers had Windows machines. But no longer.With increased popularity has come increased vulnerability. And with that, Apple...
Read more...

October might officially be National Cyber Security Awareness Month, but based on the online security reports that have come out this July, it appears that Cyber Security Awareness is actually being promoted a few months early this year. First McAfee released its report on the lack of security measures being taken by small and medium...
Read more...

Security company Finjan recently proclaimed that it detected over 1,000 different Website domains had been compromised during the first two weeks of June by a known malware toolkit, "Asprox," which has been around for over a year (according to Symantec). "… a new round of mass Web attacks has...
Read more...

Heck, if you're going to write malware, you might as well protect yourself against piracy, and copyright it, right?Professional virus writers are now selling a suite of software on the Internet with an unusual attachment: a detailed licensing agreement that promises penalties for redistributing the malicious code without permission."I just...
Read more...

Sometimes it pays to keep a low profile. Navy and Air Force pilots refer to it as flying under the radar, but IT people refer to the concept as security via obscurity. No matter what you call it, the idea is simple: if you don't draw attention to yourself, you should end up with...
Read more...

In the long battle between malware creators and companies developing and distributing anti-virus software, there seems to be a clear leader at the moment: the malware creators.This isn't entirely unexpected as one would assume that the anti-virus companies can't possibly guess all the different ways which somebody might be able to exploit...
Read more...

Mac OS X malware? It can't be! That OS always purports itself to be so safe. And they're using a favorite type of bait: porn.Intego, a Mac security software company, issued an alert Wednesday warning Mac users of the OSX.RSPlug.A malware, which it describes as a Trojan horse. Those of you familiar with mythology recognize...
Read more...

In what should probably be a surprise to none, China hosts nearly half of all the world's malware sites. The U.S. places a distant second (but we are trying harder, right?). What's more surprising is the daily number of newly detected malware sites. According to a report released Monday by antivirus company Sophos, China--including...
Read more...
Two years ago the Nopir-B worm was out "in the wild" and deleting MP3s on infected machines, and now it’s W32.Deletemusic’s turn to try doing the same: “The worm spreads via removable flash drives, reminiscent of the way viruses spread via floppy disks decades ago. That may be an attempt by the authors of the worm to bypass e-mail filters...
Read more...

The Harry Potter series of novels is popular, to say the least. It's popular enough to spawn a malware e-mail scheme. An e-mail promising an attachment that contains a copy of the latest wildly anticipated novel "Harry Potter and the Deathly Hallows" contains a virus instead. But at least it's...
Read more...