

Items tagged with security
Apparently, another one of the somewhat all-too-common malware-related problems in the U.S. military has resulted in the systems used by pilots who control U.S. Air Force drones being infected by a "keylogger." Although detected by the military's security systems, they've been unable to wipe...
Read more...
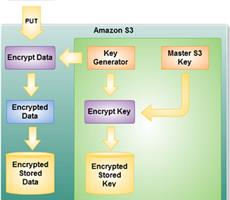
Thanks to a new Server Side Encryption feature, Amazon Web Service customers will be able to easily encrypt data stored on the company's Simple Storage Service (S3). Before this new feature was revealed, businesses had to choose an encryption algorithm, create and store keys, and "bottleneck"...
Read more...
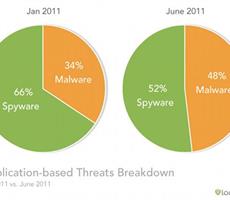
The folks at Lookout Mobile Security released the 2011 Mobile Threat Report, which offers a sobering look at the current state of mobile threats. According to the report, mobile users are more likely than ever to experience a malware...
Read more...
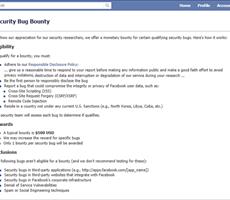
Facebook is about to get a little safer with the social networking site’s announcement that it will offer a bounty to independent researchers for any bugs they uncover, to the tune of $500 a pop (or potentially more, if you bag an especially prized bug). To receive a bounty, you have to agree to certain terms and meet specific criteria....
Read more...
Can there be too much security? If looking at America's airports, the answer is probably "yes," but if when considering online activities, the answer is probably "no." Google security engineers understand that, as they've had their fair share of security backlashes the past few years. A few...
Read more...
Well, this is some news that is sure to frustrate gamers: Ubisoft has decided that it will continue implementing its special constant-connection anti-piracy measures because, to nobody's surprise, it works. The company's restrictive digital rights management (DRM) system, which was recently...
Read more...

Whether true or not, Apple’s Mac OSX is typically perceived as being more secure than Windows. But according to Passware, Inc., a leading maker of password recovery and e-Discovery software for Federal and State agencies, law enforcement, and military organizations, among many other...
Read more...
Of all the hundreds of thousands of computer viruses, trojans, rootkits, and worms that have been written since 'Elk Cloner' first appeared in the wild in 1981, the overwhelming majority of them have targeted computer software. Attacking computer hardware directly isn't impossible now (and...
Read more...
It's like the wild west all over again, only this time we have the Internet, modern technology, and plumbing. Oh, and Microsoft isn't asking anyone to bring back a head on a platter. The Redmond sheriff is simply asking for "new...
Read more...
Mozilla is working on a project that could eliminate the need for passwords and the sign-up/verification processes on websites. Mozilla's BrowserID is an experimental way of logging in to websites. BrowserID uses the verified email protocol and aims to offer a streamlined user experience. After a user proves ownership of an email address,...
Read more...
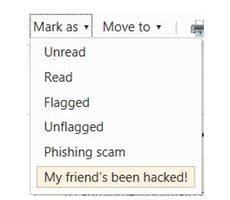
By any measure, end users are still using passwords that are far too simple. The Gawker Media hack from 2010, in fact, showed "123456" was the most common password in Gawker's database. Well, Microsoft's decided that if folks aren't going to pick strong passwords, at the very least Microsoft...
Read more...
Hackers are taking advantage of another highly publicized event to push spam on end users. In this case, Google+. Invitations to the new service are no long available, but even though the new social networking service is in "field test mode" (meaning somewhat imcomplete), an invitation to the service is a hot item. Pharmaceutical spammers...
Read more...
Computer hacking has a bad reputation, and understandably so. When one hears about organizations exposing the credit cards of millions of PSN users, there's not much argument that its criminal behavior. Against that background is cast the shadow of a new hacker convention: DEFCON Kids. DEFCON...
Read more...

Microsoft on Thrusday warned that scammers are now phoning home -- your home -- as one more way to get a fool to part with his money. The scam involves cybercriminals posing as security engineers calling people at home to tell them their PCs could be at risk for malware and offering free...
Read more...

Not long ago, we learned of an issue that affects all systems running Flash. Although most users' minds automatically think of the vulnerabilities they could be exposed to on their PC, because the BlackBerry PlayBook supports flash, this tablet is also susceptible. For this reason, RIM is releasing a new version of the BlackBerry Tablet OS...
Read more...

The Spanish National Police announced today that they've captured three individuals connected to the online hacktivist group Anonymous. According to the policía, the three are linked to attacks on multiple Spanish banks, one Italian energy company, Visa, MasterCard, and the governments...
Read more...

Paranoia. It's what makes the world go 'round. So maybe that's not precisely true in all cases, but does it not apply here? With the rampant hacking that's been going on (we're looking at you, Sony!), people near and far are suddenly...
Read more...

All it takes is a little bad publicity. Google is rolling out a fix to remedy the authToken security flaw we wrote about earlier. While Google early rolled out a client-side fix for Android 2.3.4 and higher, that left 99 percent of Android users still vulnerable. Considering how hard it is to...
Read more...

The bad news: Google's Android platform has a vulnerability that could allow the credentials used to access Google Calendar, Contacts and possibly other accounts to be stolen. The good news: Google fixed this in Android 2.3.4. More bad news: Android 2.3.4 is only on 1 percent of Android...
Read more...

Sony hardly needs any more negative PR. This is the same company that got caught installing rootkits on computers, and more recently, released a bevy of legal hounds on notorious PlayStation modder George Hotz. But folks, what Sony needs is hardly of concern at this point. Much more pressing...
Read more...

Apple is readying iOS 4.3.3 to fix the iOS location tracking "bug," where an unencrypted consolidated.db file continues to grow, and grow, and grow on the device. Apple will release the update within the next two weeks, or possibly sooner. This isn't a major release, so Apple can spring it on...
Read more...
While much attention is focused on Facebook scams and trojans involving Osama bin Laden's death, Facebook users should be aware of another new way scammers are spreading links to rogue sites. They have begun to circulate convincing links claiming to be stories from Wired News about the iPhone 5. This scam takes advantage of Facebook’s...
Read more...