

Items tagged with security

In what sounds like a scene out of one of those (well meaning, but never remotely accurate) cyber-action movies, teams of technicians from Symantec and Microsoft’s Digital Crimes unit wielding a court order from the U.S. District Court in Alexandria, Virginia, were escorted by U.S...
Read more...

Following rumors that hacktivist collective Anonymous had breached the US Federal Reserve servers this past weekend comes word from the Fed itself to acknowledge that it did in fact happen. Despite the fact that Anonymous managed to leak...
Read more...

In the cloud storage and sharing market, Dropbox is the prototypical service that everyone emulates, and LogMeIn’s new offering, Cubby, indeed bears a striking resemblance. Like Dropbox, it offers 5GB of free cloud storage that you can access, manage, and edit via a Web browser, mobile device, or synced desktop folder. If you invite...
Read more...

Social butterflies beware, there's a brand new strain of the Facebook Token Hijacker malware going around, and it preys on victims who want to score a pair of free UGGs boots. What makes this malware "special" is that it's armed with...
Read more...

Google’s Eric Schmidt has written a book in collaboration with fellow Googler Jared Cohen called The New Digital Age, and the Wall Street Journal has been reviewing it and pulled out some interesting bits to share. One of the...
Read more...

If our not-too-subtle hint a couple of weeks ago about the perils of having Java installed wasn't enough to convince you to uninstall, you should waste no time in heading on over to the official site and grabbing the latest version (7u13)...
Read more...
Concerned that hacking is on the rise? You've every right to be worried. Following recent reports from The Wall Street Journal and The New York Times surrounding intrusion from outside forces into their news systems and e-mail databases, Twitter has now affirmed a security puncture of its own...
Read more...
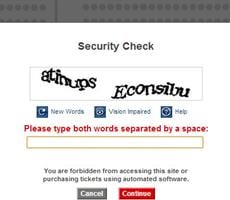
Have you ever found yourself caught in a Captcha loop? It's where you do your best to decipher strings of text that sometimes look like a bunch of hieroglyphics, only to get it wrong over and over again until finally, you punch in the correct characters and are granted to access to a site...
Read more...

On Wednesday, GitHub expanded and improved its search feature to make it easier to locate code stashed on the site by live-indexing newly uploaded code. In theory, it sounds like a nice improvement on the site’s ability to deliver...
Read more...

There are some basic rules to follow when selecting a password. For example, while we're sure your significant other is a fine person, using their name as your password is a terrible idea. Same goes for your son's birthday. The object is to select a series of characters and symbols that's nigh...
Read more...

Most of us have dozens of passwords to remember, including for multiple email accounts, Google, Facebook, online banking and credit card accounts, services like Dropbox and Evernote, and on and on, and it’s simply a pain. It can be...
Read more...
When Oracle released its Java Update 11 earlier this week, it patched several zero-day exploits that security researchers had previously identified. Nevertheless, a number of firms still recommended uninstalling Java due to a number of...
Read more...
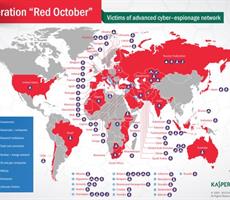
Java is a mess; Oracle’s software has become a popular target of cybercriminals, and news about Java exploits is becoming more and more common, even as the solutions Oracle provides offer little comfort. Wait, it gets worse: According to Kaspersky Labs and security company Seculert, the...
Read more...

Verizon's Risk Team has published a blog post on a mind-boggling security adventure (it's the only term that really fits) detailing just how poorly some IT workers -- including those working for "critical infrastructure" companies --...
Read more...

Software vulnerabilities are common, but it’s not every day that the Computer Readiness Team (CERT) at the U.S. Department of Homeland Security steps in and starts warning the public. Not surprisingly, Oracle jumped on the...
Read more...
Consider this a PSA: Oracle is going to patch that hole in Java, the one that security pros discovered last week. Cybercriminals were using a zero-day exploit in Oracle’s Java to deliver malware payloads, steal identities, and take over computers to force them to commit nefarious acts...
Read more...
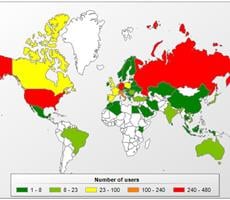
Here we go again. We're not even halfway through the first month of the New Year, and already we're being warned to disable Java. Not as a general practice, mind you (though that's not a bad idea), but because of yet another zero-day exploit spotted in the wild "There appears to be multiple ad...
Read more...

Nokia can ill-afford any missteps as it attempts to rebuild its brand into a major smartphone player, so it's a little concerning on a number of levels that it was caught intercepting Internet traffic on its phones and redirecting the data...
Read more...
The antivirus market is enormous, responsible for billions in revenue each year. That being the case, it'd be easy to believe that current offerings are quite good, but not so claims a report (PDF) by security company iMPERVA. This...
Read more...

Although it’s disturbing that there needed to be laws preventing employers and institutions of higher learning from demanding Facebook usernames and passwords from job applicants and employees, apparently the practice (or at least...
Read more...

Microsoft is currently investigating reports of a zero day bug affecting Internet Explorer 6, Internet Explorer 7, and Internet Explorer 8, the company announced in a Security Advisory. At issue is a remote code execution vulnerability...
Read more...

A couple of years ago, the Stuxnet worm went on a bit of a rampage worldwide and hit Iranian systems especially hard. Primarily, it hit industrial targets including nuclear power plants and oil rigs. Stuxnet itself has faded a bit, although it was revealed this summer that another particularly nasty piece of malware called Flame had a lot...
Read more...